 付款。
(在家觀看 = 0%,在校觀看 = 100%)
100% 在校觀看日期及時間:
自由選擇,點選以下地區觀看辦公時間及位置
課時: 30 小時
享用時期: 15 星期。進度由您控制,可快可慢。
課堂錄影導師:Larry
在校免費試睇:首 3 小時,請致電以上地點與本中心職員預約。
本課程提供在校免費重睇及導師解答服務。
(在家觀看 = 100%,在校觀看 = 0%)
100% 在家觀看日期及時間:
每天 24 小時全天候不限次數地觀看
課時: 30 小時
享用時期: 15 星期。進度由您控制,可快可慢。
課堂錄影導師:Larry
在校免費試睇:首 3 小時,請致電以上地點與本中心職員預約。
本課程提供導師解答服務。
Fortinet 是一家全球領先的網路安全公司,於 2000 年成立。Fortinet 專注於提供廣泛的網路安全解決方案,包括防火牆 (Firewall)、入侵防禦系統 (IPS)、防毒軟件、虛擬私人網路 (VPN)、以及網路流量管理工具。
Fortinet的產品和服務旨在保護企業和組織免受各類網路威脅,如惡意軟件、勒索軟件、釣魚攻擊和分散式阻斷服務攻擊 (DDoS)。
Fortinet 的盈利模式是通過銷售其硬件設備、軟件訂用服務和專業技術支援。其核心產品 FortiGate 防火牆以高性能和全面的安全功能見稱,令 Fortinet 在全球網路安全市場中佔據了重要地位。
此外,Fortinet 還提供 FortiGuard Labs 的威脅情報和安全服務,為客戶提供即時的威脅防禦和安全更新。
根據 IDC 市場研究報告,Fortinet 在全球網路安全市場中擁有顯著的市場份額,尤其是在統一威脅管理 (UTM) 和企業防火牆領域。
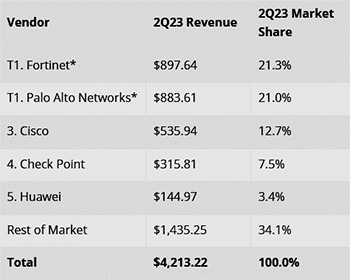
Top 5 Companies, Worldwide Security Appliance Total Market Revenue and Market Share
雖然具體市場份額數據可能會隨時間變動,但 Fortinet 在這些領域通常位列前茅,與其他領先的網路安全公司競爭,如 Cisco、Check Point 和 Palo Alto Networks。
Fortinet 透過不斷創新和擴展其產品組合,確保其在不斷變化的網路安全領域中保持領先地位。
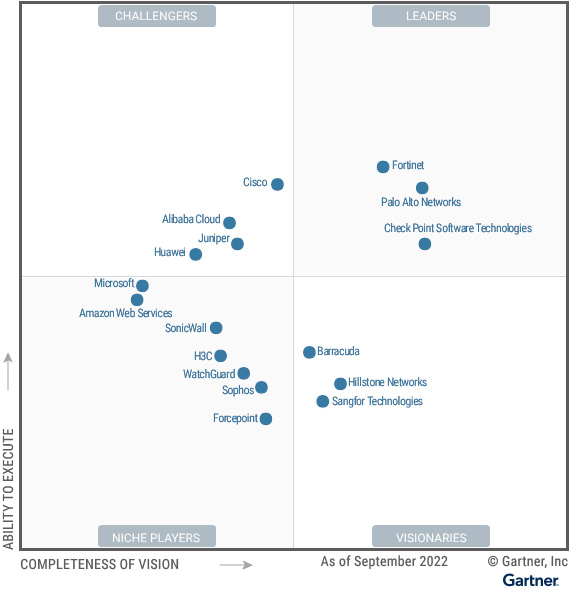
Fortinet 在全球擁有多個研發中心和辦事處,僱用了超過 13,000 名員工,是網路安全行業的三大領導者之一,詳見以下 Gartner - Magic Quadrant for Network Firewalls:
作為一家致力於網路安全的公司,Fortinet 注重推動網路安全的創新和發展,與業內其他公司和組織合作,共同應對不斷出現的網路威脅。
Fortinet (NASDAQ: FTNT) 的市值約為 583 億美元 (超過4540億港元),是全球網路安全行業的領先企業之一。根據該公司的年度財報數據顯示,其全年營收為 53 億美元,較上年同期增長 20%;毛利約為 40 億美元。
總體而言,Fortinet 在網路安全行業擁有穩健的財務狀況和強大的市場地位,並持續通過技術創新和業務拓展來推動其在市場中的競爭力。
Fortinet 的核心技術:FortiOS (本課程的主要內容)
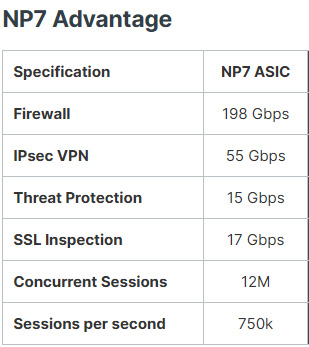
FortiGate Next Generation Firewall (NGFW) 產品採用了專用的安全處理晶片 (ASIC),並集成了自有的 FortiGuard 實驗室的威脅情報服務,提供業界領先的安全保護功能和包括加密流量在內的超高性能。
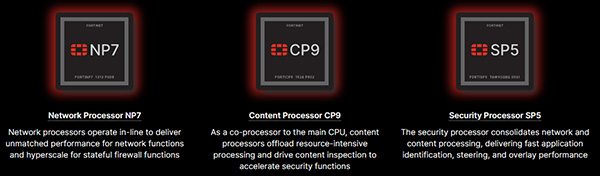
這些專用的安全處理晶片由 Fortinet 親自設計並交由 TSMC (台積電) 以成熟穩定及質素優良的 7 納米制程生產。以 NP7 為例,Fortinet 的單一安全處理晶片全過濾效能可高達 198 Gbps!
FortiGate 所提供的應用、使用者和網路視覺化大大降低了設定及監察網路安全的複雜程度,同時為你的設定提供安全評級及建議 (Security Advise),讓你能夠遵從網路安全的最佳設定 (Security Best Practice)。
網路安全工程師考慮的是如何使用 FortiGate 防火牆為其企業提供全面的威脅防護,這包括入侵防禦、Web 過濾、反惡意軟體和應用程式控制。
依據著名研究機構 Gartner 的推斷,80% 的企業流量 (Traffic Flow) 是處於被加密的狀態,而 50% 針對企業的攻擊是隱藏在加密流量中。因此,現代防火牆針對已加密的流量處理、攻擊偵測、入侵防禦、甚至是阻斷加密流量的能力及性能,在今時今日的企業顯得特別重要!
FortiOS 作為唯一的 FortiGate 防火牆作業系統,就充分發揮了 Fortinet 安全處理晶片的性能,以單一晶片每秒高達 17Gbps 的性能來處理及保護已加密的流量。部份高階型號的 FortiGate 防火牆更安裝多顆 NP7 安全處理晶片以達到更高的加密流量處理性能。
FortiOS 作業系統是 Fortinet Security Fabric 的核心
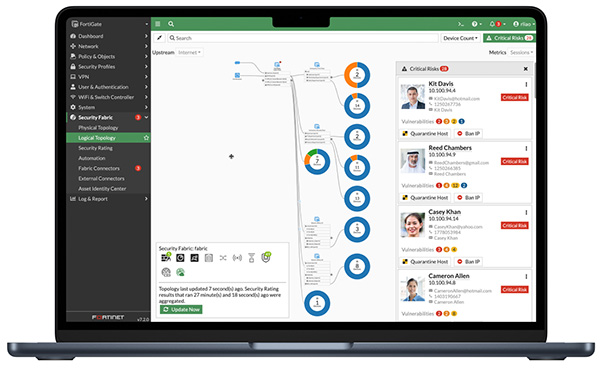
FortiOS
各機構或組織在推進數位化創新 (Digital Innovation) 的過程中,均需要確保其安全性能跟得上當今複雜而瞬息萬變的威脅。
根據 Gartner、IDC、Forester Research 及 Cisco Annual Internet Report 於 2018 至 2023 這五年期間,企業使用終端用戶設備由約 30 億增長至 50 億,可想而知網路邊緣的安全形勢是相當嚴峻的。
註: 網路邊緣 (Edge of the Network) 通常是指網路架構中接近用戶端的那一層,這裏涵蓋了終端用戶設備 (如手機、電腦)、遠端分支機構 (Branch & SOHO) 的網路設備,以及與物聯網 (IoT) 相關的裝置等,於近年出現爆炸式增長。
隨著工作模式的轉變,這些網路邊緣設備在數量上,以及它們所生產和處理數據的急速增長,網路邊界已不再像以往的集中式架構那樣清晰,而是更加分散,導致了網路邊界的碎片化。故此這要求網路安全策略必須更加適應這種去中心化的架構,從而確保所有網路邊緣的安全性。
多年來為了解決單一問題而添加各式各樣不相干的安全產品,並未考慮到整體安全性原則,導致出現各種管理上的挑戰。而快速增長的網路邊緣則加劇了這些挑戰。
以往,這些不同的解決方案是無法相互協作或分享資訊的,導致無法一致地落實安全性原則和端到端可見性。而維持和監控眾多的混合、硬體、軟體和 “X-as-a-Service” (“一切” 即服務) 解決方案也使安全團隊不堪重負。
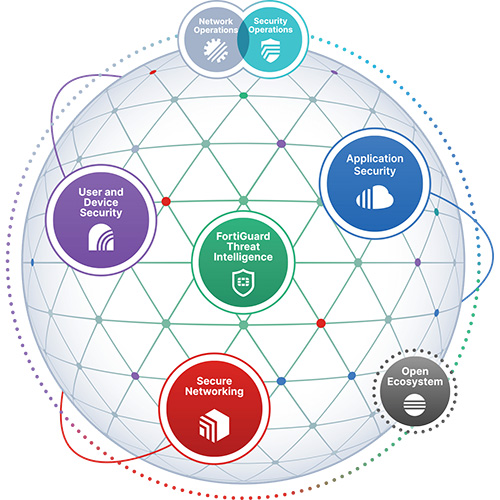
Fortinet 的 FortiOS 作業系統是 Fortinet Security Fabric 安全框架的基石,把許多技術和用例整合成了統一威脅防護解決方案 (Unified Threat Management,UTM)。
當你透過本課程學會 FortiOS UTM 解決方案,你將會為你的機構或組織帶來以下的好處:
- 靈活性和適應性:利用靈活的解決方案來處理現代設施中各種複雜的安全設定。
- 集中整合和管理:你可以將所有功能整合在一個管理控制台中進行控制。
- 高成本效益:減少了你為保護網路而投入的設備數量,顯著地節省成本。
- 提高對網路安全威脅的認識:使你的團隊能夠更好地管理高級持續性威脅和其他現代危險。
- 更快落實的安全解決方案:簡化數據處理方式,並同時使用更少的資源。
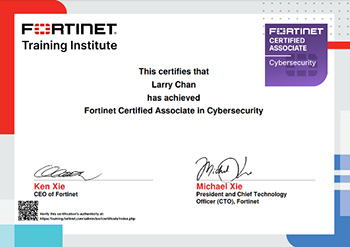
為了提升你在網路安全方面的技能及應考 Fortinet FCA 認證的能力,本課程將詳盡教授 FortiOS 的功能及 FortiGate 防火牆的設定,例如:
- FortiGate 防火牆系列及目標市場概述
- 設定不同類型的介面卡 (Interface)、網路位址轉換技術 (NAT) 和路由 (Routing)
- 防火牆策略 (Firewall Policy)
- 網路使用者身份驗證 (User Authentication)
- 檢查 SSL/TLS 流量
- 阻擋惡意軟體
- 網頁過濾 (Web Filtering)
- 設定 FortiGate 入侵防禦系統 (IPS)
- 雲端應用程式控制 (Cloud Application Control)
- 建立 IPsec 虛擬私人網路 (VPN)
- 設定 FortiGate SSL VPN
- FortiGate NGFW 系統升級、維護與監控
- 設定 Fortinet 安全架構 (Security Fabric)
FCA
完成本課程後,你不但可以考取 FCA 認證,你還可以把學會的網路安全知識及技術切實地使用於以下的 FortiGate 防火牆系列產品,並投放於你的企業環境!
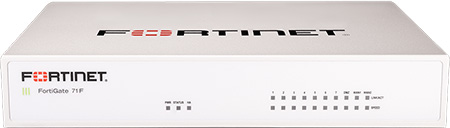
Entry Level - FortiGate 40F, 50G, 60F, 70F, 80F, 90G series
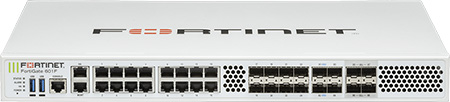
Mid Range - FortiGate 100F, 120G, 200F, 400F, 600F, 900G series
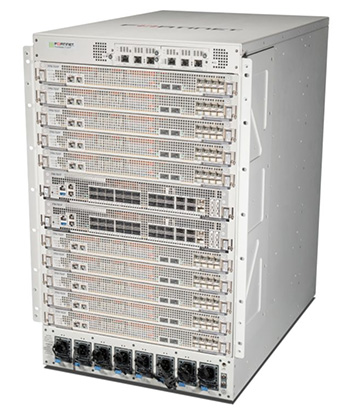
Datacenter - FortiGate 1000F, 1800F, 2600F, 3000F, 3200F, 3500F, 3700F, 4200F, 4400F, 4800F, 6001F, 6300F, 6500F, 7081F, 7121F
| 課程名稱: |
Fortinet Certified Associate Cybersecurity (FCA) 國際認可證書課程 - 簡稱:Fortinet FCA Training Course |
| 課程時數: | 合共 30 小時 (共 10 堂) |
| 適合人士: | 對電腦網路有基礎認識的任何人士。 |
| 授課語言: | 以廣東話為主,輔以英語 |
| 課程筆記: | 本中心導師親自編寫英文為主筆記,而部份英文字附有中文對照。 |
| 1. Larry Chan 親自教授: | Larry 善於控制學習節奏,深入淺出,令學員在輕鬆氣氛下,掌握電腦技巧。 |
| 2. Larry Chan 親自編寫筆記: | Larry 親自編寫筆記,絕對適合 FortiGate Operator 考試及實際工作之用。 |
| 3. 提供模擬考試題目: | 本中心為學員提供 FortiGate Operator 的模擬考試題目,每條考試題目均附有標準答案。而較難理解的題目,均會附有 Larry 的解釋。 |
| 4. 理論與實習並重: | 本中心的 FCA 課程大部份時間以實習示範形式教授,令學員真正了解及掌握FortiGate防火牆管理的重要技巧。 |
| 5. 一人一機上課: | 本課程以一人一機模式上課。 |
| 6. 免費重讀: | 傳統課堂學員可於課程結束後三個月內免費重看課堂錄影。 |
只要你於下列科目取得合格成績,便可獲 Fortinet 頒發 Fortinet Certified Network Security Expert - Level 3 (NSE 3) 國際認可證書:
|
本科目考試費用全免,Fortinet FCA 是於家中應考的非公開考試科目,而報考前考生需進行一些由 Fortinet 指定的網上程序及手續。 本中心導師將於課堂內提供通過該程序及手續的正確指示,令你順利報考免費考試。 考試題目由考試中心傳送到你要應考的電腦,考試時以電腦作答。所有考試題目均為英文,而大多數的考試題目為單項選擇題 (意即 O) 或多項選擇題 (意即 口),以及實戰題。作答完成後會立即出現你的分數,結果即考即知! 考試不合格便可於 15 日後重新報考,不限次數。欲知道作答時間、題目總數、合格分數等詳細考試資料,可瀏覽本中心網頁 "各科考試分數資料"。 |
| 課程名稱:Fortinet Certified Associate Cybersecurity (FCA) 國際認可證書課程 - 簡稱:Fortinet FCA Training Course |
1. FortiOS
1.1 混合式網狀架構防火牆
1.1.1 管理 IT 複雜性
1.1.2 網路安全技能落差
1.1.3 進階威脅興起
1.1.4 AI/ML 的角色與威脅情資 (Threat Intelligence)
1.2 混合式網狀架構防火牆中應注意事項
1.2.1 集中統一的管理
1.2.2 ASIC 型設備
1.2.3 雲原生防火牆 (Cloud Native Firewall)
1.2.4 虛擬防火牆
1.2.5 防火牆即服務 (FWaaS)
1.2.6 單一作業系統
1.3 A Brief summary of steps getting a FortiGate up and running
1.4 Setting up FortiGate for management access
1.5 Completing the FortiGate Setup wizard
1.6 Planning and configuring the MGMT, WAN, and LAN interfaces
1.6.1 Management access
1.6.2 WAN interface
1.6.3 LAN interface
1.6.4 Configuring the default route
1.6.5 Configuring the hostname
1.6.6 Ensuring internet and FortiGuard connectivity
1.7 Registering a FortiGate device
1.8 Configuring a firewall policy
1.9 Backing up the configuration
1.10 Troubleshooting your installation (Optional Knowledge)
2. Using the GUI
2.1 Connecting using a web browser
2.2 Tables
2.2.1 Filters
2.2.2 Editing objects
2.2.3 Copying rows
2.2.4 Entering Values
2.2.5 Numbers
2.3 GUI-based global search
2.3.1 Loading artifacts from a CDN
2.3.2 Accessing additional support resources
2.3.3 Command palette
2.4 Recovering missing graphical components
3. Using the CLI
3.1 Connecting to the CLI
3.1.1 Console connection
3.1.2 SSH access
3.2 CLI basics
3.2.1 Help
3.2.2 Shortcuts and key commands
3.2.3 Command tree
3.2.4 Command abbreviation
3.2.5 Adding and removing options from lists
3.2.6 Environment variables
3.2.7 Special characters
3.2.8 Using grep to filter command output
3.2.9 Language support and regular expressions
3.2.10 Screen paging
3.2.11 Changing the baud rate
3.2.12 Editing the configuration file
3.3 Command syntax
3.3.1 Notation
3.3.2 Optional values and ranges
3.3.3 next
3.3.4 end
3.4 Subcommands
3.4.1 Table subcommands
3.5 Permissions
4. Configuration and Management Tools
4.1 FortiExplorer Go and FortiExplorer
4.1.1 FortiExplorer Go
4.2 Getting started with FortiExplorer
4.3 Connecting FortiExplorer to a FortiGate with WiFi
4.4 Configure FortiGate with FortiExplorer using BLE
4.5 Running a security rating
4.6 Migrating a configuration with FortiConverter
5. Product Registration with FortiCare
5.1 FortiCare and FortiGate Cloud login
5.2 FortiCare Register button
5.3 Transfer a device to another FortiCloud account
5.4 Deregistering a FortiGate
6. FortiGate models
6.1 Differences between models
6.2 Low encryption models
6.2.1 Reasons for Using Low-Encryption Models
6.2.2 Practical Limitations of Low-Encryption Models
6.3 LEDs
6.3.1 More about Port LEDs
6.3.2 Alarm levels
6.4 Proxy-related features not supported on FortiGate 2 GB RAM models
6.5 Upgrading from previous firmware versions
7. Dashboards and Monitors
7.1 Using dashboards
7.2 Viewing device dashboards in the Security Fabric
7.3 Creating a fabric system and license dashboard
7.3.1 Example
7.4 Dashboards
7.4.1 Resetting the default dashboard template
7.4.2 Status dashboard
7.4.3 Updating system information
7.4.4 Viewing Fabric devices
7.4.5 Viewing administrators
7.4.6 Viewing logs sent for remote logging source
7.4.7 Resource widgets
7.4.8 Viewing session information for a compromised host
7.4.9 Network dashboard
7.4.10 DHCP monitor
7.4.11 IPsec monitor
7.4.12 IPsec monitor
7.4.13 SSL-VPN monitor
7.5 Assets & Identities
7.5.1 Assets
7.5.2 Assets and filtering
7.5.3 Adding MAC-based addresses to devices
7.5.4 Firewall Users monitor
7.5.5 WiFi dashboard
7.5.6 FortiAP Status monitor
7.5.7 Clients by FortiAP monitor
7.5.8 Health status
8. FortiView Monitors
8.1 Optimal and Comprehensive Template
8.2 Core FortiView monitors
8.3 Adding FortiView monitors
8.4 Using the FortiView interface
8.4.1 Real-time and historical charts
8.4.2 Data source
8.4.3 Drilldown information
8.5 Enabling FortiView from devices
8.6 FortiView sources
8.7 FortiView Sessions
8.8 FortiView Top Source and Top Destination Firewall Objects monitors
8.9 Viewing top websites and sources by category
8.10 Cloud application view
8.11 Configuring the Cloud Applications monitor
8.12 Monitoring network traffic without SSL deep inspection
9. Deploying FortiGate-VM
9.1 FortiGate-VM models and licensing
9.2 Deployment package contents
9.3 Permanent trial mode for FortiGate-VM
10. Firewall Policy
10.1 Firewall Policy Parameters
10.2 Configurations in the GUI
10.3 Configurations in the CLI
10.3.1 Firewall anti-replay option per policy
10.3.2 Deny matching with a policy with a virtual IP applied
10.3.3 Hardware acceleration
10.3.4 TCP Maximum Segment Size (MSS)
10.3.5 Adjusting session time-to-live (TTL)
10.3.6 Policy views
10.3.7 Policy match
10.4 Services
10.4.1 Predefined services
10.4.2 Custom services
10.4.3 Service groups
11. Local-in policy
11.1 Configuring the local-in policy
11.2 Virtual patching on the local-in management interface
11.3 Implicit deny rule
11.4 TTL policies
11.5 Internet service as source addresses
11.6 Logging local traffic per local-in policy
12. DoS Policy
12.1 DoS anomalies
12.2 DoS policies
13. Access control lists
14. Interface Policies
15. Source NAT
15.1 Static SNAT
15.2 Dynamic SNAT
15.2.1 IP pool types
15.2.2 One-to-one
15.2.3 Fixed port range
15.2.4 Port block allocation
15.2.5 NAT64 in FortiGate firewall
15.2.6 IP pools and VIPs as local IP addresses
15.3 Central SNAT
15.3.1 To enable central SNAT from the GUI
15.3.2 To configure central SNAT using the CLI
15.3.3 Fine-tuning source port behavior
15.4 Configuring an IPv6 SNAT policy
16. Destination NAT
16.1 Configuring VIPs
16.2 Viewing VIP overlap in security rating reports
16.3 IP pools and VIPs as local IP addresses
16.4 Virtual IP with services
17. Virtual Server Load Balancing
17.1 SSL/TLS offloading
17.2 Virtual server requirements
17.2.1 Virtual server types
17.2.2 Load balancing methods
17.2.3 Health check monitoring
17.2.4 Session persistence
17.2.5 Real servers
17.2.6 Sample of HTTP load balancing to three real web servers
17.2.7 Virtual server load balance multiplexing
18. Security Profile Inspection Modes
18.1 Flow mode inspection (default mode)
18.2 Proxy mode inspection
18.3 Inspection mode feature comparison
18.3.1 Feature comparison between Antivirus inspection modes
18.3.2 Feature comparison between Web Filter inspection modes
18.3.3 Feature comparison between Email Filter inspection modes
18.3.4 Feature comparison between DLP inspection modes
19. Antivirus
19.1 Antivirus introduction
19.1.1 Protocol comparison between antivirus inspection modes
19.1.2 Other antivirus differences between inspection modes
19.2 Antivirus techniques
19.2.1 Content disarm and reconstruction
19.2.2 Virus outbreak prevention
19.2.3 External malware block list
19.2.4 EMS threat feed
19.2.5 AI-based malware detection
19.3 Configuring an antivirus profile
19.4 Proxy mode stream-based scanning
19.5 TCP windows
19.6 Flow mode stream-based scanning
19.7 Databases
19.8 FortiSandbox database
20. Web Filter
20.1 Web filter techniques
20.2 Configuring a web filter profile
20.3 FortiGuard filter
20.4 Blocking a web category
20.5 Allowing users to override blocked categories
20.6 Issuing a warning on a web category
20.7 Authenticating a web category
20.8 Customizing the replacement message page
20.9 Category usage quota
20.10 Restrict YouTube and Vimeo access
20.11 Block invalid URLs
20.12 URL filter
20.13 Block malicious URLs discovered by FortiSandbox
20.14 Web content filter
20.15 Credential phishing prevention
21. Video Filter
21.1 Configuring a video filter profile
21.2 YouTube API key
21.3 Filtering based on FortiGuard categories
21.4 Verifying that the video is blocked
21.5 Troubleshooting and debugging
21.6 Filtering based on YouTube channel
21.6.1 Identifying the YouTube channel ID
21.7 Filtering based on title
21.8 Filtering based on description
22. DNS filter
22.1 DNS filter behavior in proxy mode
22.2 Configuring a DNS filter profile
22.3 FortiGuard category-based DNS domain filtering
22.4 Botnet C&C domain blocking
22.5 Botnet C&C IPDB blocking
22.6 DNS safe search
22.7 DNS over QUIC and DNS over HTTP3 for transparent and local-in DNS modes
23. Inline CASB
23.1 Privilege control
23.2 Safe search
23.3 Tenant control
23.4 UTM bypass
23.5 Microsoft CoPilot Commercial Data Protection
24. Intrusion prevention
24.1 Signature-based defense
24.1.1 IPS signatures
24.1.2 Protocol decoders
24.1.3 IPS engine
24.1.4 IPS sensors
24.1.5 IPS filters
24.1.6 Custom and predefined signature entries
24.1.7 Overriding the default action
24.1.8 Policies
24.2 IPS configuration options
24.2.1 Malicious URL database for drive-by exploits detection
24.2.2 IPS signature rate count threshold
24.2.3 Botnet C&C
24.2.4 Extended IPS database
24.2.5 IPS engine-count
24.2.6 OT threat definitions
24.2.7 Fail-open
24.2.8 IPS buffer size
24.2.9 Session count accuracy
24.2.10 Protocol decoders
24.3 SCTP filtering capabilities
24.4 IPS signature filter options
24.4.1 Hold time
24.4.2 Viewing on hold information in the GUI
24.4.3 CVE pattern
24.4.4 IPS sensor attributes
24.5 IPS with botnet C&C IP blocking
24.6 IPS sensor for IEC 61850 MMS protocol
24.6.1 MMS (Manufacturing Message Specification) usage scenario
24.6.2 How FortiGate helps in securing MMS/ICCP communications
24.6.3 IPS signatures for the operational technology security service
25. VPN
25.1 Site-to-site VPN
25.1.1 Create a Phase 1 Interface
25.1.2 Phase 2 configuration
25.1.3 Adding routes for Route-Based VPN
25.1.4 Configuring Security Policy to allow traffic to pass through VPN tunnel
25.2 VPN IPsec troubleshooting
25.2.1 Understanding VPN related logs
25.3 IPsec related diagnose commands
25.4 VPN and ASIC offload
26. Remote Access VPN
26.1 FortiClient as dialup client
26.2 L2TP over IPsec
26.3 FortiGate as dialup client
27. Virtual Domains
27.1 VDOM overview
27.1.1 Multi-VDOM mode
27.1.2 Global settings
27.1.3 Global and per-VDOM resources
27.1.4 Management VDOM
27.1.5 VDOM types
27.1.6 Administrator roles and views
27.1.7 Inter-VDOM routing
27.1.8 Best practices
27.2 Enable multi-VDOM mode
27.2.1 To enable VDOMs in the GUI:
27.3 Management VDOM
27.4 Global and per-VDOM resources
27.5 Creating Traffic Type VDOM
27.6 Create per-VDOM administrators
27.7 Backing up and restoring configurations in multi-VDOM mode